- Enforcement
- Markets & Trading
- Governance & Accountability
Two million alerts, one set of eyes.
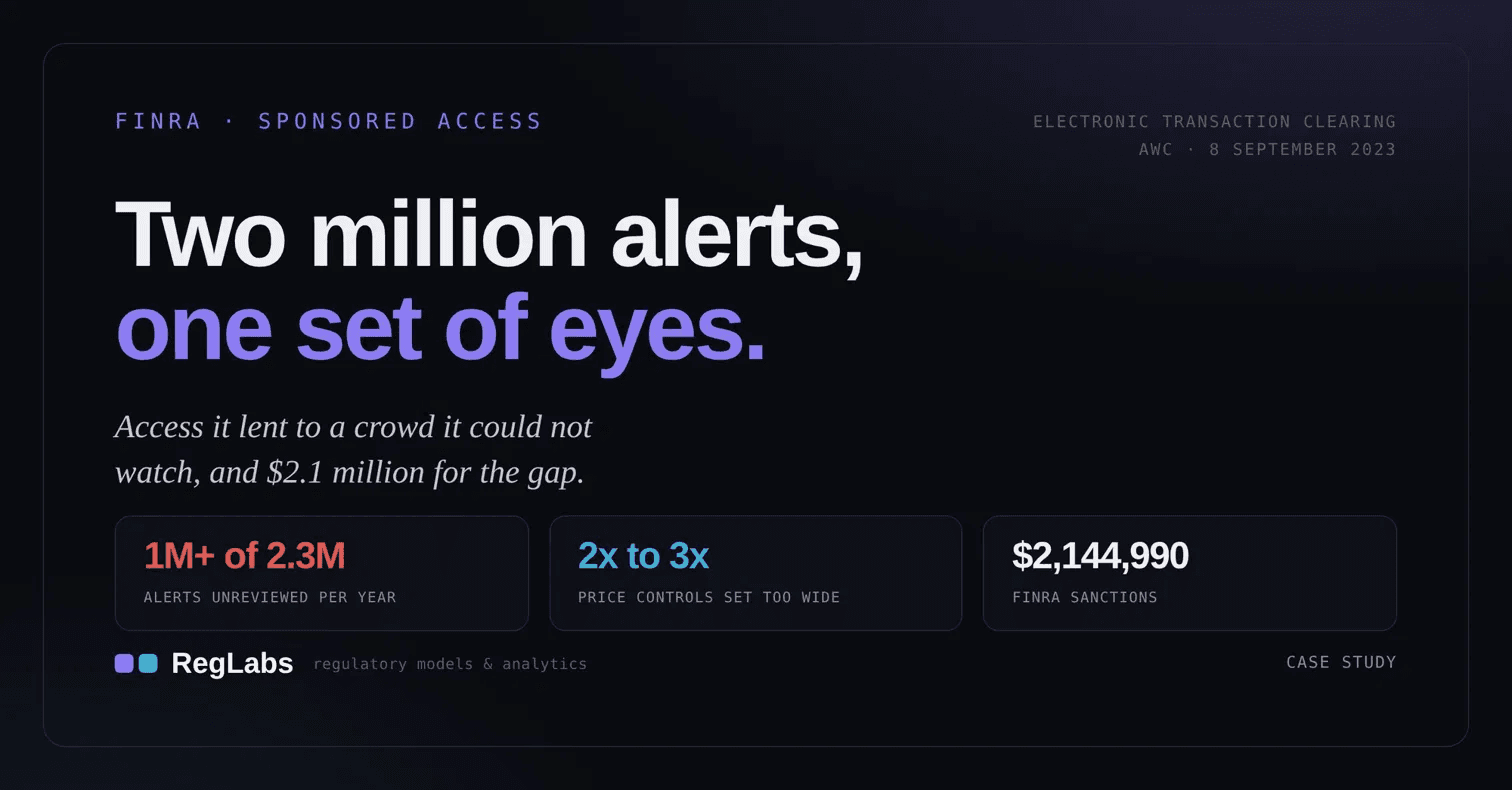
A small clearing firm lent its market access to foreign broker-dealers and crowds of overseas day traders, then generated 2.3 million surveillance alerts a year and gave one person the job of reading them. FINRA priced the gap at $2.1 million.
A $2.1 million penalty for access it could not supervise
On 8 September 2023, FINRA accepted a Letter of Acceptance, Waiver and Consent from Electronic Transaction Clearing, Inc., a Dallas clearing firm with fewer than 25 registered representatives, resolving a sprawling set of control failures for total monetary sanctions of $2,144,990. ETC provided execution, clearing, and stock-lending services, and, at the center of this case, sponsored access to foreign and domestic broker-dealers and institutional customers, including several customers made up of hundreds of individual foreign-based day traders.1
The firm consented to findings on three fronts at once, and the three are really one story. Its surveillance for manipulative trading was unreasonable. Its market-access risk controls under the SEC's Market Access Rule were unreasonable. And its anti-money-laundering program was unreasonable. Each failure has its own rule, its own time period, and its own set of facts, but they share a single cause: ETC had taken on more access-provision than it had the capacity, or the will, to supervise, and it closed the gap by under-staffing its controls and handing responsibility for them to the very customers they were meant to police.
Three control programs, one root cause
The rules differ. The cause is identical: access granted faster than it could be supervised.
Source: FINRA, Letter of Acceptance, Waiver and Consent , No. 2017055657501, Electronic Transaction Clearing, Inc. (CRD No. 146122), accepted 8 September 2023.
This study treats the case as what it really is: a complete anatomy of the sponsored-access, or gatekeeper, problem, the risk that a firm lends its regulatory membership and market connectivity to others and then cannot see or stop what flows through it. It walks the crowd of foreign day traders ETC enabled, the single reviewer assigned a million alerts, and the controls handed to the parties they were meant to police, and then lifts each failure into the discipline it violated: why a control is only a claim about the attention a firm can actually pay; why generating alerts you cannot review is worse than not generating them; why a control delegated to the risk it governs is no control; why a price band set two to three times too wide is a gate that never closes; why a certification is not evidence the work was done; and why red flags received and unworked are the most damning failure of all. The closing sections place it in a history of four prior fines for the same conduct, and in the forward problem of supervising access at machine scale.
What sponsored access actually is
Most firms that trade on an exchange are members of it, vetted, capitalized, and subject to its rules. Sponsored access is the arrangement that lets a firm that is not a member reach the market anyway, by routing its orders through a member firm's connection and under the member's regulatory identity. The sponsoring firm, here ETC, is the one the exchange and the regulator hold responsible. Its membership, its credit, and its compliance obligations are what stand behind every order the sponsored client sends. In exchange for fees, the sponsor lends the client a door to the market that the client could not open on its own.
That arrangement is useful and entirely legitimate, and it is also, by its nature, a concentration of risk in a single place: the sponsor. Because the client trades under the sponsor's identity, everything the client does, every erroneous order, every manipulative pattern, every suspicious flow, is legally the sponsor's to prevent, detect, and report. The sponsor is the only party positioned to see the client's activity against the market as a whole, and the only party the regulator can hold to account for it. This is precisely why the SEC's Market Access Rule, Exchange Act Rule 15c3-5, exists: it was written to stop firms from renting out their market access without maintaining the risk-management controls and supervisory procedures to govern what passes through. The rule treats the sponsor's controls not as an internal nicety but as the condition of being allowed to provide access at all.
The structural point to hold onto is that in a sponsored-access business the firm's controls are the product's safety mechanism, and they have to scale with the access granted. A sponsor that doubles the number of clients, or takes on a client that is really hundreds of traders, has multiplied the activity it is responsible for supervising, and its controls, its surveillance, its risk limits, its AML monitoring, have to grow to match. If they do not, the firm has sold more access than it can supervise, which means it has become a conduit through which others can reach the market faster than anyone is watching. ETC is the case study in exactly that mismatch, and the Market Access Rule is the law it was written to satisfy and did not.
The crowd behind the curtain
The nature of ETC's clients is what turns this from a paperwork case into a market-integrity one. ETC did not provide access to a handful of institutions it knew well. It provided sponsored access to foreign and domestic broker-dealers and institutional customers, and, as FINRA found, several of those institutional customers were themselves comprised of hundreds of individual foreign-based day traders. Behind a single account that ETC carried on its books sat a crowd of overseas traders, each entering their own orders, under ETC's regulatory identity, into the U.S. market.1
Consider what that structure means for the firm's obligations. Each of those hundreds of individual traders could enter orders that mark the open or the close, that wash against one another, that layer or spoof, that move a thinly-traded stock. From the market's point of view, all of it was ETC's flow, sent under ETC's name, and ETC was the only firm positioned to surveil it. The volume alone was enormous, which is why ETC's surveillance systems generated more than two million alerts a year. But volume was not the hardest part. The hardest part was that the activity came from many hands the firm did not directly know, trading in ways that only coordinated, cross-trader surveillance could catch, and a firm that takes on that kind of client has signed up for exactly that kind of surveillance.
This is the gatekeeper's bargain, and ETC took the upside without the obligation. A firm that sponsors a crowd of foreign day traders is monetizing its market access and its regulatory standing, and in return it is accepting responsibility for watching a population of traders larger and less visible than its own staff. The fee is immediate; the surveillance burden is continuous and scales with the crowd. When the FINRA findings describe ETC's clients, they are not providing color; they are establishing the size of the duty the firm had assumed, against which every subsequent failure of capacity has to be measured. ETC had let in a crowd, and then watched it with almost no one.
One reviewer, a million alerts
ETC had surveillance systems. It had two of them: a vendor-provided platform the findings call System 1, and an in-house platform called System 2, run together to detect manipulative trading. The systems worked well enough to generate the alerts. What ETC did not have was anyone to read them. From May 2017 through December 2019, the firm delegated the daily review of all System 1 alerts, including every inquiry and follow-up investigation, to a single person. Review of System 2's reports was handled by one or two reviewers. By 2018, the systems were producing more than one million alerts per year, and the total reached roughly 2.3 million, of which the firm failed to review more than one million.1
The surveillance the firm generated, and the attention it could pay
Some reviews were delayed by six months. The reviewers assigned to System 2 from spring 2018 had no prior relevant experience.
Source: FINRA, Letter of Acceptance, Waiver and Consent , No. 2017055657501, Electronic Transaction Clearing, Inc. (CRD No. 146122), accepted 8 September 2023.
The findings add detail that makes the staffing failure worse than the raw numbers. There were significant delays in the reviews that did happen, in some cases of six months, by which point any manipulative pattern had long since run its course. First-level reviewers were permitted to close surveillance alerts for potentially manipulative trading without any oversight or supervision by a firm principal, so a single junior reviewer's decision to dismiss an alert was final. And the people assigned to review System 2's alerts from the spring of 2018 onward had no prior relevant experience. The firm had, in effect, built a detection engine capable of surfacing manipulation across a crowd of traders, and then placed behind it the thinnest, least-supervised, least-experienced review function it could, and let most of the output pile up unread.
It is worth being precise about what this is and is not. It is not a case of a firm that lacked surveillance technology; ETC had two systems and they worked. It is a case of a firm that treated the technology as the control and the review of its output as an afterthought, to be absorbed by whoever happened to be available, in whatever time was left. The alerts were generated. The firm simply never resourced the human judgment that an alert exists to trigger, and the result was a surveillance program that was, functionally, a very expensive way of documenting manipulation it did not act on.
A control is a claim about the attention you can actually pay
The staffing failure points to the first and most generalizable discipline of the case, and it is one that firms systematically underweight because it is about people rather than systems: a control is not a piece of software or a written procedure; it is a claim that the firm will pay a certain amount of attention to a certain kind of risk, and that claim is only true if the attention actually exists. A surveillance system that generates alerts no one reads is not a control that is working badly; it is not a control at all, because the detection is only the first half, and the half that matters, the human judgment that reviews, investigates, and acts, was never staffed.1
The reason this is so easy to get wrong is that the technology creates a powerful illusion of coverage. A firm that buys a surveillance platform, configures its scenarios, and watches alerts appear on a dashboard has visible, tangible evidence that it is monitoring, and that evidence is genuinely reassuring to a board, an auditor, or a regulator asking "do you surveil for manipulation." The answer is yes, the system is there, the alerts are generating. What that evidence conceals is the capacity question: of the alerts generated, how many are actually reviewed, by how many people, with what experience, within what time. ETC could truthfully say it had surveillance; it could not say that the surveillance produced any attention, because one person cannot meaningfully review a million alerts, and the firm had assigned roughly that. The gap between the system existing and the attention being paid is exactly where ETC's manipulation surveillance lived, and it is invisible to any assessment that counts systems rather than measuring throughput.
Size the control to the risk, or shrink the risk to the control
The discipline is to treat review capacity as a measured, governed control in its own right, sized explicitly to the volume of activity the firm has taken on, and to treat a persistent backlog as a control breach rather than an operational inconvenience. A firm that generates two million alerts and can review two hundred thousand has a one-point-eight-million-alert control failure, continuously, and it has only two honest responses: increase the capacity to match the risk it has accepted, or reduce the risk, by tuning the alerts, by shedding the clients, or by declining the access, to a level its capacity can actually cover. What it cannot do, and what ETC did, is generate the alerts, staff a fraction of the review, and let the rest accumulate unread, because that produces the worst of all outcomes: the firm has manufactured a record that it detected suspicious activity and did nothing about it. The number that matters in a surveillance program is never how many alerts it generates; it is how many it reviews to a reasoned, documented conclusion, on time, and a firm that is not measuring and governing that number does not know whether it has a control or a backlog with a dashboard.
The blind spots in the net
Even where ETC did review, the net it was reviewing had holes, and the holes were in exactly the patterns a crowd of coordinated day traders was most likely to exploit. The findings catalogue a series of coverage gaps that meant whole categories of manipulation could not have been caught no matter how diligent the reviewer, because the surveillance was not designed, or was quietly redesigned, to see them.1
- The multi-MPID blind spot. ETC's clients could enter orders through multiple market participant identifiers, but only two of the firm's twelve surveillance reports accounted for trading by a client using more than one MPID. A trader who spread activity across identifiers, which is exactly how wash trades and prearranged trades are hidden, could trade against themselves and have it go undetected, because the surveillance looked at each identifier in isolation.
- No marking-the-open surveillance at all. The firm lacked any reasonable surveillance specifically designed to detect marking the open until the end of October 2019, well into the relevant period. For years, one of the classic manipulation patterns simply was not watched for.
- A client excluded by a coding error. A coding issue excluded an entire algorithmic client from ETC's prearranged-trading surveillance, so that client's orders were never screened for that pattern, silently, until the error was found.
- Surveillance narrowed until it stopped working. At one point ETC narrowed its marking-the-close surveillance parameters to the point that the surveillance became unreasonable, tightening the thresholds until the pattern it existed to catch could slip beneath them.
These are different failures with one shared character: each is a gap in what the surveillance could see, as opposed to a gap in who reviewed it. The multi-MPID blind spot is a design flaw that assumes a trader uses one identifier when the firm had explicitly allowed many. The missing marking-the-open scenario is an absent control. The coding exclusion is a silent data gap of exactly the kind that defeats even a well-staffed program. And the narrowing of the close parameters is calibration drift toward uselessness, a scenario loosened or tightened until it no longer fires. A reviewer, however diligent, cannot catch what the system never surfaces, which means coverage completeness, whether the surveillance is actually watching for every pattern the firm's activity could produce, is a control that sits upstream of, and is independent of, the capacity to review. ETC failed both: it could not see all the patterns, and it could not review the alerts for the patterns it could see.
Alerts you generate but cannot review
There is a counterintuitive point buried in the million unreviewed alerts that deserves to be drawn out, because it inverts how firms usually think about surveillance volume: generating alerts you cannot review is, in an important sense, worse than not generating them at all. A firm with no surveillance for a pattern has a detection gap, which is a serious problem. A firm that surveils, generates alerts, and then leaves them unreviewed has something more damaging: a documented record that it was told about potentially manipulative activity and did nothing, created by its own systems and sitting in its own files.1
The distinction matters legally and practically. When FINRA examined ETC, it did not have to prove that manipulation had occurred and the firm missed it through some subtle gap; it could point to the firm's own alerts, more than a million of them, generated by the firm's own systems, flagging potentially manipulative trading, and never reviewed. The alerts are the firm's own contemporaneous evidence that its systems saw something worth looking at, and the absence of review is the firm's own record that it did not look. A firm cannot argue it had no reason to suspect a pattern when its surveillance system raised an alert on that exact pattern and the firm filed the alert away unread. The unreviewed alert converts a question about whether the firm should have known into a demonstrated fact that the firm was told and did not act.
Reconcile what you generate against what you can resolve
The discipline this produces is twofold and specific. First, a firm must reconcile alert generation against review capacity continuously, treating any gap between the two as a live, reportable control failure rather than a queue to be worked down someday. The relevant metric is the ratio of alerts resolved to alerts generated, over time, and a ratio well below one, sustained, is a flashing indicator that the program has lost control of its own output. Second, a firm that finds it is generating far more alerts than it can review faces a genuine design choice that it must make deliberately rather than by neglect: either resource the review to match, or re-tune the surveillance so that it generates fewer, higher-quality alerts that the available reviewers can actually clear. Tuning down alert volume is legitimate and often necessary, but it has to be a reasoned calibration decision, documented and defensible, not the de facto result of a backlog that everyone ignores. What is never acceptable is the ETC outcome, in which the system generates a flood, the firm reviews a trickle, and the remainder accumulates as unread evidence of suspicious activity the firm was warned about. An alert you cannot review is not surveillance. It is a liability your own systems are writing down in real time.
The controls it handed to the risk
The most structurally revealing failures in the case are the ones where ETC did not merely under-resource a control but handed the control to the very party it was supposed to govern. Across several of the findings, the pattern is the same: rather than exercise a supervisory judgment itself, ETC relied on the people it was meant to be supervising, or on a lone unsupervised reviewer, to perform the firm's own control function.1
Who was supposed to control, and to whom ETC gave it
In each row, the firm's own control was performed by the party it was meant to check, or by no one in particular. The judgment the firm owed was never exercised by the firm.
Source: FINRA, Letter of Acceptance, Waiver and Consent , No. 2017055657501, Electronic Transaction Clearing, Inc. (CRD No. 146122), accepted 8 September 2023.
The clearest instance is the market-access risk controls. Under Rule 15c3-5, ETC was responsible for setting and maintaining the financial risk controls, credit limits, order-size and price checks, that governed a sponsored client's trading. For at least one market-access customer, ETC improperly delegated responsibility for establishing those controls to the client's introducing broker, and did so without adequately analyzing or reviewing the controls the introducing broker set. The firm that bore the regulatory responsibility for the controls let a party closer to the client decide what they would be, and then did not check them. The same posture appears in ETC's history: in the prior matter, the firm had improperly relied on the systems of a non-broker-dealer customer to take the protected-quotation snapshots that Regulation NMS required ETC to take. And it appears in the surveillance function, where a first-level reviewer could close a manipulation alert with no principal oversight, so the firm's supervisory judgment was exercised, finally and without review, by its most junior staff.
You cannot outsource a control to the party it polices
The delegation failures crystallize into one of the sharpest and most portable principles in all of controls governance: a control exists to constrain someone, and it cannot be performed by the person it is meant to constrain, because then it constrains no one. When ETC let a client's introducing broker set the client's risk limits, the limits were set by a party whose interest ran toward more access, not less. When it relied on a non-broker-dealer customer's systems to capture the quotations that governed that customer's own order protection, it let the subject of the control run the control. The form of supervision was preserved; the substance, an independent party exercising judgment against the interest of the party being supervised, was gone.1
This is distinct from the ordinary and legitimate practice of relying on vendors, service providers, or other firms to perform operational tasks. A firm can outsource the mechanics of a control, the software, the data feed, the processing, and remain fully responsible for the judgment the control embodies, provided it retains the independence to set, review, and override what the outsourced mechanics produce. What a firm cannot do is outsource the judgment itself to the party the control is meant to check, because supervision is, by definition, an adversarial function: it exists precisely because the supervised party's interests may diverge from compliant behavior, and handing it the controls aligns the controls with the divergence. The introducing broker setting its client's risk limits is not a neutral administrator; it is a party with a commercial relationship to the client and an incentive toward looser limits, and ETC's failure to analyze or review what that broker set meant the firm had delegated not just a task but its entire protective function to someone structurally disinclined to exercise it.
Delegate the work, never the judgment
The discipline follows directly: a firm may delegate the work of a control but must retain the judgment, and it must retain it with genuine independence from the party being controlled. In a sponsored-access business this is concrete and testable. The sponsor sets the risk limits, on its own analysis, and documents why; it does not accept the limits the client or the client's broker proposes without independent review. The sponsor performs its own regulatory obligations, the quotation snapshots, the surveillance, the AML monitoring, on systems and with people it controls, not on the subject's infrastructure. And where review judgments are made, closing an alert, approving a limit, waiving a check, they are made or overseen by someone with the seniority and independence to say no, not by a lone first-level reviewer whose decisions are final and unsupervised. The test a firm should apply to every control is simple: who actually exercises the judgment this control represents, and do they have an interest in it failing. If the answer is the party being controlled, or no one in particular, the control is decorative. ETC's controls were, across its risk limits, its quotation obligations, and its alert dispositions, exactly that.
Price bands set never to bind
Where ETC did maintain its own market-access price controls, it set them so wide that they could not do their job. Rule 15c3-5 requires a firm providing market access to have controls reasonably designed to prevent the entry of erroneous orders, and a price check is the archetypal such control: it rejects an order priced so far from the market that it is almost certainly a mistake. ETC had price controls for five sponsored-access clients, and the findings describe them as not reasonably designed, because the thresholds were too permissive to be effective.1
The reference points, and where ETC set the gate
For securities above $25, thresholds ran two to three times the Clearly Erroneous Execution levels; for NMS stock above $3, two times the Limit Up-Limit Down bands.
Source: FINRA, Letter of Acceptance, Waiver and Consent , No. 2017055657501, Electronic Transaction Clearing, Inc. (CRD No. 146122), accepted 8 September 2023.
The specifics make the looseness concrete. For securities priced above $25, ETC's price-control thresholds were, in some instances, two to three times the Clearly Erroneous Execution numerical thresholds, the levels at which the exchanges themselves will break a trade as obviously mistaken. For certain NMS stocks priced above $3, the thresholds were two times the Limit Up-Limit Down price bands, the regulatory guardrails that pause trading when a stock moves too far too fast. In other words, ETC's controls would let through orders priced well beyond the point at which the market's own definitions say an order is erroneous. A price check calibrated to two or three times the erroneous-order reference is not a check that occasionally lets a bad order through; it is a check positioned so that a genuinely erroneous order, by the market's own standard, sails underneath it.
This is the same calibration failure that recurs across market-access enforcement, and the lesson is identical wherever it appears: a control that exists but is set so loosely that it will not fire on the event it names is worse than a visible gap, because it manufactures the false confidence that the risk is covered. ETC could report that it had erroneous-order price controls, and it did; a review that checked for the existence of such controls would find them. Only a review that asked the operative question, are these controls calibrated tightly enough to actually reject an erroneous order, would have found that they were set two to three times beyond the level that defines one. The right benchmark for a price control is the market's own definition of an erroneous order, and a control set multiples looser than that benchmark has been calibrated, whether by design or by drift, to never bind.
The limit with no rationale
Alongside the loose calibration sat a quieter failure that the Market Access Rule treats as its own violation: ETC did not document the rationale for the financial risk controls it set. Before late 2018, the firm failed to document its reasoning when establishing and adjusting clients' credit controls and erroneous-order controls. At the end of 2018 it created a log recording the establishment of and adjustments to clients' credit thresholds, which is the kind of record the rule contemplates, yet it still failed, in instances after that, to document the rationale for the credit and erroneous-order control settings and the adjustments it made to them.1
It is tempting to read a documentation requirement as bureaucratic, a demand for paperwork that does not change what the controls actually do. That reading misunderstands why the rule requires it, and the misunderstanding is instructive. The rationale behind a risk limit is not administrative trivia; it is the evidence that the limit was set by a reasoned process rather than by whim, convenience, or the client's preference. When a firm documents why a credit threshold is what it is, what the client's activity justifies, what analysis supports it, what would prompt a change, it creates a record that the limit reflects a deliberate judgment about risk. When a firm cannot produce that rationale, as ETC could not, the limit is unmoored: there is no way to tell whether it was set at a defensible level or simply set wherever was easiest, no way to review whether an adjustment was justified, and no way for a supervisor or a regulator to assess whether the control embodies any judgment at all. The undocumented limit is the calibration failure's twin: the loose price band showed a control set too wide to work, and the missing rationale showed the firm could not even demonstrate that its risk limits were set by thought rather than by default.
A limit you cannot justify is a limit you cannot defend
The discipline is that every risk-limit setting and every adjustment to it should carry a documented, contemporaneous rationale, not as a compliance formality but as the artifact that makes the limit reviewable and the control auditable. The test is whether, for any limit the firm has set, it can answer three questions from its own records: why is the limit at this level, what analysis supports it, and what changed when it was adjusted. A firm that can answer those has limits that embody judgment and can be defended, improved, and held accountable. A firm that cannot, like ETC after it had even built a log and still left the rationale blank, has limits that are numbers without reasons, which a regulator will read, correctly, as controls that were never genuinely governed. In the sponsored-access context the point is sharper still, because the whole premise of the rule is that the sponsor exercises independent risk judgment over its clients, and a risk limit with no documented rationale is the record of a judgment that was never made.
Certified, not performed
The Market Access Rule contains a backstop designed precisely for firms like ETC: it requires the chief executive officer, or an equivalent officer, to certify annually that the firm's risk-management controls and supervisory procedures comply with the rule. The certification is meant to force senior accountability, to ensure that someone at the top has looked, confirmed the controls work, and put their name to it. ETC's written procedures required an annual review of the effectiveness of its risk-management controls and supervisory procedures, and the related CEO certification. The firm did not do the review. It did not review any of its risk controls for 2017, and reviewed some, but not all, of them for 2018 and 2019, and the certification was signed over that record.1
This is the attestation failure, and it recurs across enforcement because the attestation is one of the most relied-upon and least reliable controls in financial services. A certification measures nothing by itself; it is a statement by the firm that the work was done, and its value depends entirely on whether the work behind it actually happened. When a CEO certifies that the firm's market-access controls have been reviewed for effectiveness, and the firm has in fact reviewed none of them for one year and only some for two others, the certification has not detected or prevented anything. It has produced a clean annual record, signed at the most senior level, that is contradicted by the firm's own conduct. The certification, far from being the backstop the rule intended, became another document asserting that a control was operating while it was not.
Certify the work, not the intention
The discipline the rule is reaching for, and that ETC defeated, is that a certification must rest on completed, evidenced work, and the signing officer must demand that evidence before signing. The point of putting the CEO's name on the annual review is to create a person with the incentive and the authority to insist that the review actually occurred, in full, before they attest to it, because they bear the consequence if it did not. A certification signed over an incomplete review inverts that logic: it uses the form of senior accountability to launder an absence of work, giving the firm, the regulator, and the board a signed assurance that the controls were checked when they were not. The honest version is unglamorous: before certifying, the officer confirms that every control in scope was in fact reviewed, sees the evidence of the review and its findings, and signs only to what was done, not to what was supposed to be done. A certification is only as good as the diligence it attests to, and a certification over work that did not happen is not a control, it is a misstatement at the top of the firm, which is why the findings reach ETC's books-and-records obligations as well as its market-access ones.
The alert that never became a report
The third front was anti-money-laundering, and it failed in the same shape as the surveillance: the firm detected potential problems and did not act on them, and it had no mechanism to ensure that detection turned into the action the law requires. ETC failed to establish and implement reasonably designed AML policies and procedures to detect and report suspicious activity. It failed to review over a million of the alerts its systems generated, the same under-capacity that crippled its manipulation surveillance, and it failed to reasonably respond to red flags for the purpose of deciding whether to file a Suspicious Activity Report. And then there was a gap at the very end of the process that is worth isolating, because it is a control failure in miniature.1
The findings state that ETC had no written procedure to confirm that a SAR was actually filed once the firm had determined that a transaction met the filing threshold. As a result, the firm failed to file SARs in certain instances in which it had identified suspicious activity. Read that carefully: these were not cases where the firm missed the suspicious activity. These were cases where the firm saw it, concluded it met the threshold for a report, and then did not file the report, because nothing in the process closed the loop between the decision to file and the filing itself. The detection worked, the judgment was made, and the required action simply fell through a gap where a control should have been.
Connect the control that detects to the control that acts
This is a distinct and widely applicable discipline: a detection control and an action control are two different things, and a firm must build the connection between them, because detecting a problem and deciding to act on it are worthless if the action is not then verified to have occurred. The SAR process has three stages, detect the suspicious activity, decide it warrants a report, file the report, and a failure at any stage defeats the whole. ETC's gap was at the handoff from decision to filing: it had made the determination and had no control confirming the determination was carried out. The fix is a closed loop, a control that tracks every filing decision through to a confirmed, recorded filing, and flags any decision that has not resulted in one. The principle generalizes well beyond AML to any process where a control's job is to trigger a required action: the detection and the decision are not the end of the control, the completed action is, and a firm that does not verify the action has built a process that can recognize exactly what it is obligated to do and then fail to do it, with no one the wiser. An identified-but-unfiled SAR is the purest example, a firm that knew what the law required, decided it was required, and did not do it.
Red flags, received and unworked
The most damning thread running through all three fronts is not that ETC failed to detect problems, but that it was repeatedly told about them, by its own systems and by outside regulators, and did not act. Beyond the million unreviewed internal alerts, the findings record that a self-regulatory organization issued written warnings about potential manipulative trading by at least six of ETC's clients. These were not ambiguous internal signals; they were external, specific notices from a regulator that named the firm's clients and the concern.1
ETC's response establishes how slowly the firm moved even when the warning came from outside. After the warnings, the firm began terminating one identified client and placed two others, the findings' Client A and Client B, under heightened surveillance. It was only after additional SRO warnings about potentially manipulative orders that ETC terminated Client A and Client B. The pattern is of a firm that acted, eventually, but only under repeated external pressure, and only after a second round of warnings about clients it had already been told about and merely watched more closely. The red flags were received. The firm's response to them lagged, and in the interval the flagged activity continued under ETC's access.
A red flag is an obligation, not a notification
The discipline is that a red flag, whether raised by an internal system or delivered by an outside regulator, is not an item of information to be noted; it is an obligation to investigate and, where warranted, to act, within a timeframe proportionate to the risk. The failure to conduct reasonable follow-up on known red flags is a recurring finding in enforcement precisely because noticing is psychologically and operationally easy and acting is hard: acting means confronting a paying client, escalating, potentially terminating a revenue relationship. A firm whose culture or whose incentives make it reluctant to act on red flags will find ways to keep noticing them without ever doing anything, placing a client under heightened surveillance rather than terminating, watching rather than reporting, until the regulator forces the issue. ETC's sequence, an SRO warning, heightened surveillance, a second SRO warning, finally termination, is the signature of a firm that treated red flags as notifications to be managed rather than obligations to be discharged. When an outside regulator has to warn you twice about the same clients before you act, your red-flag process is not a control; it is a delay mechanism, and the activity you were warned about ran under your access the whole time it operated.
Trading through the quote
One strand of the case is narrower and more technical than the rest, but it illustrates the same theme, a control that depended on data the firm did not reliably capture, fixed only when a regulator asked. Regulation NMS includes an order-protection rule that forbids trading through a better-priced protected quotation displayed on another exchange. Intermarket sweep orders are a mechanism for complying with it: to use one correctly, a firm must take snapshots of the protected quotations across the market so it can satisfy the rule's conditions. From September through November 2018, and again from July 2019 through February 2020, ETC did not take reasonable steps to ensure its ISOs did not trade through protected quotes.1
The scale came from the firm's sponsored-access flow. Because of a system coding issue, ETC failed to take snapshots of protected quotations for approximately 8.5 million ISOs routed by a single sponsored-access client in the 2018 window, resulting in trade-throughs of protected quotations. In the later window, the failure recurred for approximately 150,000 ISOs. And the resolution is the detail that ties it to the rest of the case: ETC activated a pre-order ISO block, the control that would have prevented the trade-throughs, only after a FINRA inquiry. The firm had the technical ability to block non-compliant ISOs; it implemented the block in response to the regulator's question, not on its own initiative, after millions of orders had already traded through protected quotes.
This episode rhymes with ETC's history in a way the findings make explicit. In the prior ISO matter, from July 2014 through March 2015, the firm had been censured and fined an aggregate $40,000 for related failures, and in that matter it had improperly relied on the systems of a non-broker-dealer customer to take the protected-quotation snapshots. The 2018 and 2019 failures are the same control, failing again, years later, through a different mechanism, and remediated again only under regulatory pressure. A control that depends on reliably capturing market data is only as good as the data capture, and a firm that fixes it only when asked has not learned the lesson of the control; it has learned the lesson of the inquiry.
Told four times already
None of this was new to ETC, and the history is what makes the 2023 sanction read less like a first offense than like the latest bill for a condition the firm had been treating symptomatically for years. The findings catalogue a sequence of prior FINRA and SRO actions against ETC for the same categories of failure at issue here, and laid end to end they describe a firm that had been penalized repeatedly, across every front, and had not fixed the underlying problem.1
Fined for the same failures, again and again
Roughly $1.3 million in prior fines across the same categories, before the $2.1 million that followed.
Source: FINRA, Letter of Acceptance, Waiver and Consent , No. 2017055657501, Electronic Transaction Clearing, Inc. (CRD No. 146122), accepted 8 September 2023.
Read the sequence and the lesson is the one that recurs through every recidivist enforcement record: ETC remediated the specific findings of each prior action without fixing the condition that produced them. A $125,000 AML fine in 2016, a $250,000 AML fine for suspicious-trading deficiencies, an $875,000 fine touching supervision and market-access controls, a $40,000 ISO fine, each was a response to a particular surfaced failure, and each left intact the underlying reality that the firm's controls across surveillance, market access, and AML were under-resourced and over-delegated relative to the sponsored-access business it was running. The same weaknesses that produced the earlier fines produced the 2023 one, expressed through different specific failures, because the firm had treated each enforcement action as a discrete problem to close rather than as evidence of a structural mismatch between its business and its control capacity. A firm that answers each finding by fixing the named instance, while leaving the capacity and delegation problems that generated it in place, guarantees the next finding, and the escalating sequence of fines, culminating in a $2.1 million sanction, is what that guarantee costs.
The broader lesson: access you cannot supervise is access you should not grant
The enduring lesson of the ETC case is a single proposition that applies to any firm that provides access, capacity, or a credential to others: your controls must scale with the access you grant, and access you cannot supervise is access you should not grant. ETC's business was lending its market access and its regulatory identity to foreign broker-dealers and crowds of overseas day traders. The access scaled; the controls did not. The firm generated millions of surveillance alerts and staffed one reviewer, set risk limits it did not calibrate or document, delegated its own obligations to the parties it was policing, certified reviews it had not performed, and left identified suspicious activity unreported. Every one of those is the same failure in a different costume: the firm had taken on more responsibility than it had built the capacity to meet, and it closed the gap by not looking.
The disciplines that would have changed the outcome are the ones this study has drawn out, and none of them is exotic. Size the control to the risk you have accepted, or shrink the risk to the control, and treat review capacity as a measured control with a backlog that counts as a breach. Reconcile what your systems generate against what you can actually resolve, because an alert you cannot review is a liability your own systems are writing down. Retain the judgment of every control, with genuine independence, even when you delegate its mechanics, because a control performed by the party it polices is no control. Calibrate limits against the market's own definition of the harm, not multiples looser, and document the rationale for every one, because a limit you cannot justify is a limit you cannot defend. Certify only the work that was actually done. Connect the control that detects to the control that acts, so that an identified obligation is verified to have been met. And treat every red flag, internal or external, as an obligation to act within a timeframe matched to the risk. Each is a way of closing the gap between the access a firm grants and the supervision it provides, and that gap is the whole of the ETC case.
The forward view: access at machine scale
The reason the lesson is becoming more urgent, not less, is that the access firms provide is growing faster and operating faster than human supervision naturally scales. Sponsored access, direct market access, and the provision of connectivity to crowds of underlying traders already generate alert volumes, millions a year at a firm of fewer than 25 people, that no proportionate human review function can absorb, and the trend is toward more access, more automation, and more underlying participants behind each sponsor. In that environment the capacity discipline becomes the central one, because the honest choices sharpen: a firm either builds genuinely scalable supervision, which increasingly means automated, continuously-tested surveillance and risk controls that can match machine-scale flow, or it limits the access it grants to what it can actually watch. What it cannot do, and what the economics will keep tempting firms to do, is take the fees for providing access at scale while supervising it at the scale of one reviewer with a backlog. The automation that lets a small firm grant vast access is the same automation that must be turned on its own flow to supervise it, and a firm that automates the access without automating the oversight has simply built the ETC failure faster. The gatekeeper's duty does not shrink as the gate widens and the crowd grows; it is precisely then that the watching has to be built to scale, because a gate that opens at machine speed and is watched by no one is not access. It is exposure, for the firm and for the market behind it.
What this case is really about
Three control programs failed together, because none had the capacity behind it
ETC did not lack systems; it lacked the attention, the independence, and the calibration to make its systems into controls. It generated 2.3 million manipulation alerts a year and reviewed them with one or two people, leaving over a million unread. It set market-access price controls two to three times too wide, documented no rationale for its risk limits, and handed a client's controls to the client's own introducing broker. It certified market-access reviews it had not performed. And it left identified suspicious activity unreported because nothing confirmed a SAR was filed. Three rules, three programs, one cause: a sponsored-access business supervised at the scale of a backlog. The $2.1 million followed roughly $1.3 million in prior fines for the same failures.
Where it broke
- Over 1 million of ~2.3 million annual manipulation alerts unreviewed, by one or two staff, with six-month delays
- Coverage gaps: multi-MPID blind spot, no marking-the-open surveillance until late 2019, a client excluded by a coding error
- Market-access price controls set two to three times the erroneous-order reference; risk-limit rationale undocumented
- A client's risk controls delegated to its introducing broker; quotation snapshots relied on a non-broker-dealer's systems
- CEO certified 15c3-5 reviews that were not performed; SARs unfiled where suspicious activity was identified
- Red flags on at least six clients acted on only after repeated SRO warnings; four prior fines for the same conduct
What sponsored access requires
- Review capacity sized to alert volume, with any sustained backlog treated as a control breach
- Surveillance coverage complete across every pattern the flow can produce, including multi-MPID and open/close
- Price and risk controls calibrated to the market's own erroneous-order reference, with a documented rationale
- The judgment of every control retained independently, never delegated to the party it polices
- Certifications signed only over completed, evidenced reviews; a closed loop from SAR decision to confirmed filing
- Every red flag, internal or regulatory, worked as an obligation within a risk-matched timeframe
Trade Surveillance Governance agent
Tests the firm's manipulation scenarios, their design, parameters, calibration, data sources, and overall alert health, so a multi-MPID blind spot, a missing marking-the-open scenario, a client excluded by a coding error, or a review backlog of a million alerts is surfaced as a program-design finding rather than discovered by an examiner.Trading Risk Controls analyst
Reviews the market-access control stack, control design, effectiveness, calibration, parameters and thresholds, and alert statistics, so price bands set two to three times the erroneous-order reference, undocumented risk-limit rationale, and controls delegated to an introducing broker are caught and corrected, the exact 15c3-5 gaps a CEO is required to certify against.AML Governance Analyst
Reviews the AML program's control design, calibration, data sources, and alert handling, and the closed loop from a SAR determination to a confirmed filing, so suspicious activity that is identified is actually reported rather than left in an unreviewed queue.Five ways RegLabs keeps the gate as wide as the watch
This case study is an independent analysis prepared by RegLabs for educational and informational purposes, based on FINRA's public Letter of Acceptance, Waiver and Consent concerning Electronic Transaction Clearing, Inc. (accepted 8 September 2023). It is not legal advice and does not reproduce the AWC in full. All figures and quotations are drawn from the public record; any characterizations are those of RegLabs. Company and regulator names are used for identification and commentary only.